
Introduction
Cybersecurity threats are becoming increasingly complex as scammers develop more convincing methods to target individuals and businesses.
From fraudulent login alerts to sophisticated phishing campaigns attackers continuously look for opportunities to steal sensitive information and gain unauthorized access to digital accounts.
At the same time, organizations adopting artificial intelligence AI must consider new security risks associated with enterprise models and autonomous agents.
Preventing account takeover and strengthening AI security require a proactive approach. Individuals need to understand how to recognize suspicious messages while businesses must test their AI systems against potential attacks before deploying them in real-world environments.
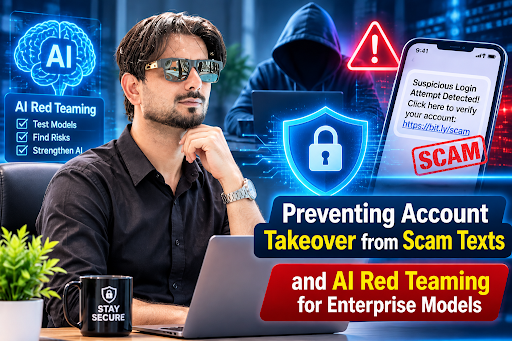
Understanding Account Takeover Through Scam Text Messages
Account takeover occurs when an attacker gains unauthorized access to someone’s online account often by stealing login credentials, passwords or authentication codes.
Scam text messages are among the common techniques used to achieve this objective.
These messages may appear to come from trusted companies financial institutions, or online platforms.
They often contain urgent warnings about suspicious login attempts account restrictions, or security problems.
Their purpose is to create panic and encourage recipients to click malicious links or provide confidential information.
Recognizing these warning signs is essential. Users should avoid clicking unfamiliar links, sharing one-time passwords, or responding to unexpected security requests.
Instead, they should independently visit the official website or application to check whether an account security issue actually exists.
Understanding how to verify suspicious login messages and prevent account takeover can help users identify fraudulent communications protect their credentials and reduce the likelihood of unauthorized account access.
Practical Strategies for Protecting Online Accounts
Individuals and businesses can reduce account takeover risks by following several basic cybersecurity practices.
- Enable Multi-Factor Authentication
Multi-factor authentication adds another layer of protection beyond passwords. Even if attackers obtain login credentials additional verification can make unauthorized access more difficult.
- Use Strong and Unique Passwords
Reusing passwords across multiple platforms increases security risks. Password managers can help users create and maintain unique credentials for different accounts.
- Recognize Phishing Attempts
Unexpected messages containing urgent requests, suspicious links, or unusual attachments should always be treated carefully. Verifying the sender through official communication channels is a safer approach.
- Monitor Account Activity
Regularly reviewing login notifications, connected devices, and account activity can help users identify unusual behavior before it develops into a serious security incident.
Why Enterprise AI Models Need Red Teaming
While traditional cybersecurity focuses on protecting networks, applications, and user accounts, artificial intelligence introduces additional security challenges.
Enterprise AI models can process sensitive information interact with external applications, and perform automated tasks.
Autonomous AI agents may also access tools, databases and business workflows.
Without appropriate security controls, these capabilities can create opportunities for exploitation.
AI red teaming involves systematically testing AI systems to discover weaknesses before attackers can exploit them.
Security professionals simulate potential attacks, examine model responses and evaluate whether existing safeguards work as intended.
For organizations developing advanced AI solutions an AI red teaming course for models and autonomous agents can provide valuable knowledge about identifying vulnerabilities, evaluating model behavior, and understanding security risks associated with autonomous systems.
Important Areas of AI Security Testing
Effective AI red teaming should examine several important areas.
- Prompt Injection: Testing whether malicious instructions can manipulate model behavior or override intended restrictions.
- Data Leakage: Identifying whether an AI system exposes confidential information through its responses.
- Unauthorized Tool Access: Evaluating whether autonomous agents can perform actions beyond their intended permissions.
- Model Reliability: Testing how systems respond to unexpected inputs, misleading information, and adversarial scenarios.
- Security Controls: Checking whether monitoring, access restrictions, and protective mechanisms operate correctly.
These evaluations help businesses understand their security weaknesses and improve the reliability of AI-powered applications.
Combining Account Protection with AI Security
Traditional account security and AI red teaming may address different technical challenges, but both support the same objective: reducing digital risks.
Individuals can protect themselves by recognizing scam messages, securing login credentials, and monitoring account activity. Organizations can complement these practices by conducting regular security assessments, testing AI models, and establishing clear access-control policies.
A comprehensive cybersecurity strategy should also include employee awareness training, incident response procedures, regular system updates, and continuous monitoring.
Conclusion
Preventing account takeover requires awareness strong authentication and careful handling of suspicious communications. Meanwhile organizations adopting artificial intelligence must understand the security risks associated with enterprise models and autonomous agents.
By combining responsible account protection practices with structured AI red teaming, individuals and businesses can create a stronger defense against evolving digital threats.
A proactive security strategy helps protect sensitive information improve system reliability, and build greater confidence in modern digital technologies.
